A morning read
Today in Paris, Microsoft announced the next stage of Microsoft Sovereign Cloud. Satya Nadella shared it, Douglas Phillips wrote the detail, and a new whitepaper, Microsoft Sovereign Cloud in Europe, sat behind it. I read all three before the sun was fully up.
Ten months ago, I wrote about Microsoft’s investment in Canada in Canada’s AI Investment Moment. I ended that piece with a line I still believe:
“AI infrastructure doesn’t run on theory. It runs on systems. And systems need stewards.”
Reading today’s announcement, I had a quiet sense of recognition. This one wasn’t about building capacity. It was about the stewardship layer arriving.
What was announced
The core idea is simple. Sovereignty is not one setting. It is a range of control, applied workload by workload.
Microsoft organizes that range into three areas:
- Sovereign Public Cloud adds controls on top of Azure for residency, encryption, operator access, policy and continuity.
- Sovereign Private Cloud runs Microsoft services on customer-operated hardware through Azure Local, connected or fully disconnected. That includes Microsoft 365 Local and Foundry Local for AI.
- Sovereign Partner Ecosystem adds independently operated national partner clouds, such as Bleu in France and Delos Cloud in Germany, plus specialized local partners.
The details are where it gets interesting. Customer Lockbox and just-in-time access put customers in the approval path when Microsoft engineers need access. A Production Touch Ledger creates tamper-evident records of that access. A new Sovereign Control Panel is coming to show sovereignty posture, gaps and continuity readiness in one place.
One note before going further: this launch, and the whitepaper behind it, are European in scope. Several controls, like Data Guardian, are rolling out for the EU and EFTA. That matters for how a Canadian reader should take it.
What I noticed: this is governance vocabulary
Read the announcement again and listen to the words. Access. Authorization. Approval. Audit. Continuity. Exit.
These are not infrastructure words. They are the words of the people who run things. They belong to anyone who has had to answer, in a steering meeting, who changed what and on whose authority.
The conversation under Satya’s post said the same thing in its own way.
Within an hour, a few themes stood out:
- Lock-in. If an organization gains control over where its data lives, how easily can it still leave?
- Legal reach. Some asked whether any US-headquartered provider can offer absolute sovereignty, given laws like the US CLOUD Act.
- Several people pointed out that sovereignty now includes what AI agents can access and what actions they are allowed to take.
One comment stayed with me. It noted that surviving a disconnection is only half the test. The harder half comes when systems reconnect: can the organization reconstruct which actions were authorized, what changed, and which state can be trusted?
That is not a hardware question. It is a governance question. It is an audit trail, a decision record, and someone accountable for both.
The Canadian context
Canada is not in today’s announcement. But Canada is very much in this conversation.
In December 2025, Microsoft announced a $7.5 billion expansion of its Canadian cloud and AI capacity, alongside a digital sovereignty plan for Canada. Its commitments included keeping Canadian data in Canada, challenging government demands for Canadian government customer data where legally possible, and defending continuity of service for Canadian government customers.
Meanwhile, Ottawa is deciding what “sovereign” will mean in practice. Shared Services Canada has launched a procurement process for Sovereign Canadian Cloud capabilities that prioritizes Canadian-owned and controlled providers. The definition it lands on will likely shape purchasing well beyond the federal government.
The debate around that definition is real, and both sides make serious points:
- Control first. The ITIF argues that Canada doesn’t need to own the cloud, it needs to control it: who can access sensitive systems, whether services survive disruption, and whether workloads can move.
- Ownership matters. Others, including the Canadian Shield Institute, argue that data location alone is not enough, and that buying through a foreign provider’s Canadian subsidiary does not make the technology Canadian.
- The legal question remains open. No tenant setting resolves the reach of foreign law. That is a matter for policy, contracts and courts.
I am not going to pick a side on ownership. That is a policy decision for Canadians and their government, and it deserves more care than a blog post can give it.
Where MYT stands: the layer both sides need
What I can offer is a view from the layer that both sides of the debate depend on.
Whoever owns the infrastructure, someone still has to:
- decide who has access, when, and with whose approval
- govern what agents and automations are allowed to do
- keep an audit trail that holds up under scrutiny
- plan for continuity, and for exit, before either is needed
That is operational governance. In practice, it is PMO work: ownership, controls, evidence, escalation, and a clear record of decisions.
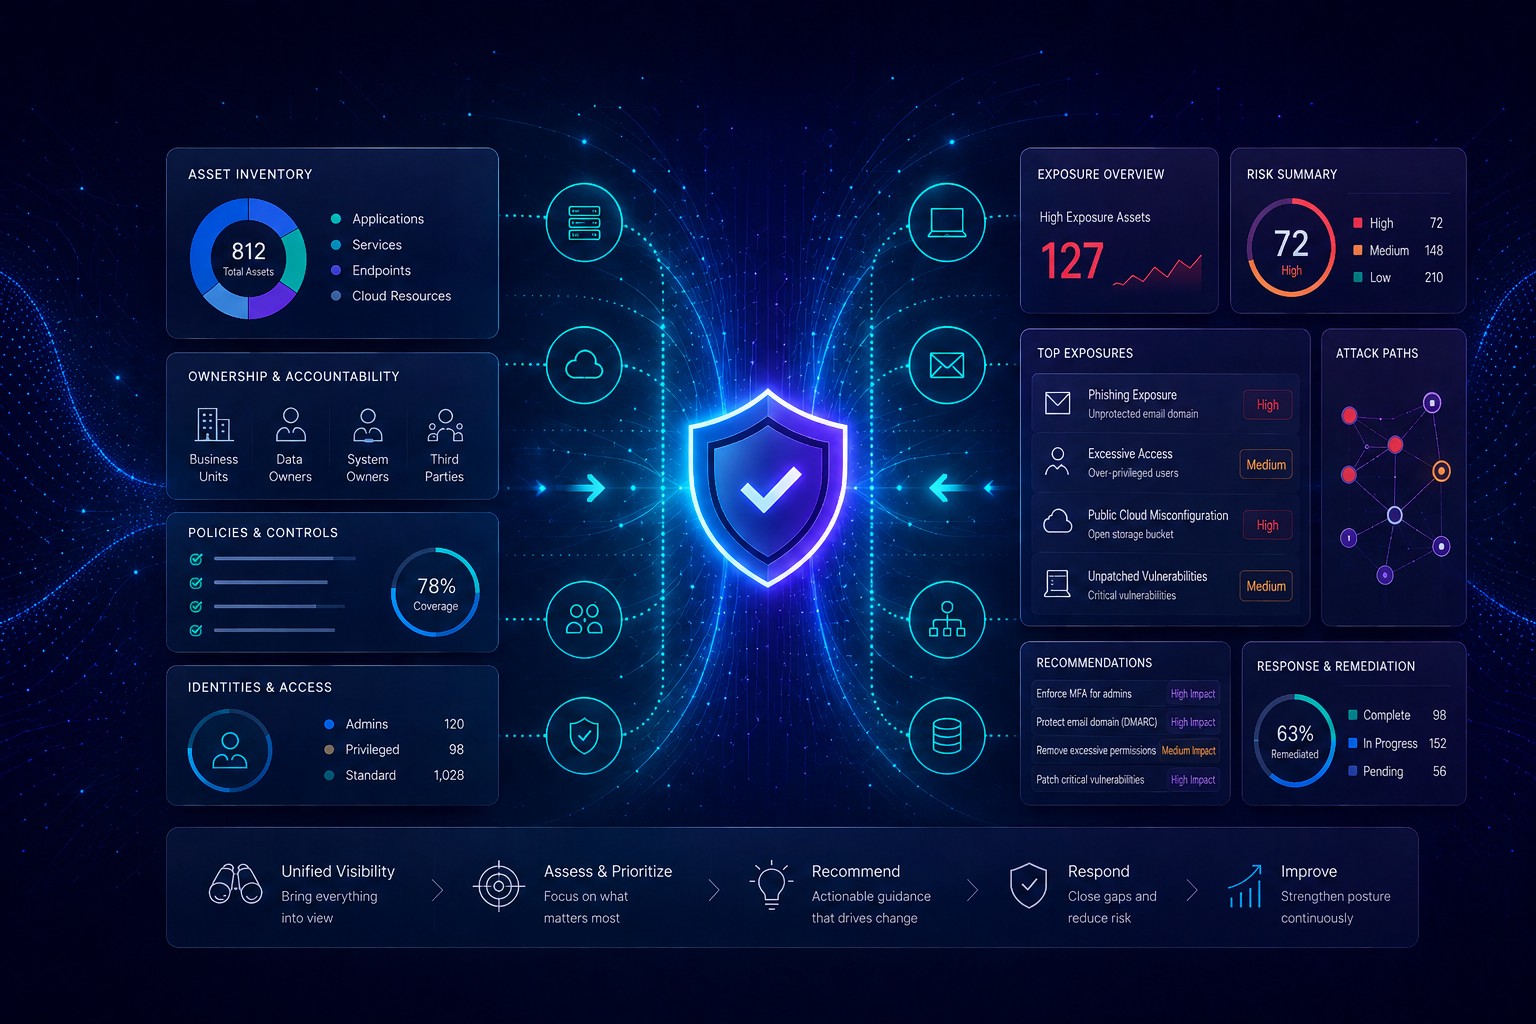
It is also the thread running through the MYT Governance Lab. The series moved from CoE visibility, to native governance, to delivery control, to security posture, and most recently to the Portfolio Control Tower, where agentic tools still answer to a human decision trail. Each chapter asked the same question at a wider scale: who is stewarding these systems, and can they prove it?
Sovereignty is that question at the national scale.
“Sovereignty isn’t something you buy. It’s something you operate.”
What’s next: the Sovereignty Readiness chapter
So I am going to test it.
The next chapter of the MYT Governance Lab will take the controls described in the European whitepaper and ask a simple question of each one: what can a Canadian organization actually do with it today?
I will work in my own environment, with mock data, the same way I built the earlier chapters.
Each control will land in one of three columns:
- Can do: available and configurable now, such as Canadian data residency, operator access approval, privileged access on a just-in-time basis, audit logging, and governance over Power Platform and Copilot Studio agents.
- Partial: possible with some setup or cost, such as a sovereign landing zone restricted to Canadian regions, or customer-managed encryption keys.
- Can’t do (and why): European-only services, hardware-based private cloud, or questions no configuration can answer.
I am not presenting this as finished expertise in a new field. It is learning in public, with the receipts attached, which is how this whole series has worked from the start.
A personal note
The timing of this feels right in a personal way, too. In a couple of weeks, I am moving to Ottawa.
It is a move I have been working toward for a long time. Ottawa is where so much of this conversation will be decided: the definitions, the procurements, and the long, careful work of operating what gets built.
In December, I wrote that Canada was choosing to participate as a builder, not just a consumer. I still believe that. And builders need stewards.
More soon, from Ottawa.
______________________________________________________________________________________________________________________
Sources
- Microsoft, Advancing digital sovereignty with greater control and choice, October 20, 2026
- Microsoft, Microsoft Sovereign Cloud in Europe (whitepaper), October 2026
- Satya Nadella, LinkedIn post and public comment thread, October 20, 2026
- Manage Your Tech, Canada’s AI Investment Moment, December 21, 2025
- Manage Your Tech, From Delivery Control to the Portfolio Control Tower, September 2026
- BetaKit, Microsoft to spend $7.5 billion on AI data centre expansion with pledge to protect Canada’s “digital sovereignty”, December 10, 2025
- ITIF, Rethinking Cloud Sovereignty: Canada Doesn’t Need to Own the Cloud—It Needs to Control It, September 10, 2026
- The DropTimes, Canada’s Federal Cloud Procurement Draws Sovereignty and Lock-In Scrutiny, August 10, 2026
Written with AI assistance as part of the MYT Governance Lab series. The ideas, editorial review and final judgment are my own.
______________________________________________________________________________________________________________________